FedRAMP announces Class G pilot for agency-operated shared clouds
The January 2027 pilot targets agency-provided offerings; responsibility text remains a non-final preview.
FedRAMP / U.S. General Services AdministrationSource checked Nov 17, 2026
Official Sources. Practical Context.
Coverage focuses on contracting developments tied to ISSO, RMF, security control assessment, vulnerability analysis and security policy analysis. Earlier general contracting coverage and company commentary remain available in the archive with their original dates and wording.
42 published articles. The historical archive preserves 24 original company posts across 21 articles. Identical archive posts share one article with all recorded links.
The January 2027 pilot targets agency-provided offerings; responsibility text remains a non-final preview.
DOJ’s settlement resolves contract-specific allegations; there has been no determination of liability.
FedRAMP explains migration evidence and reporting exemptions for applicable cloud offerings.
Updated joint guidance gives federal security and acquisition teams practical questions for evaluating suppliers’ cryptographic dependencies and transition plans.
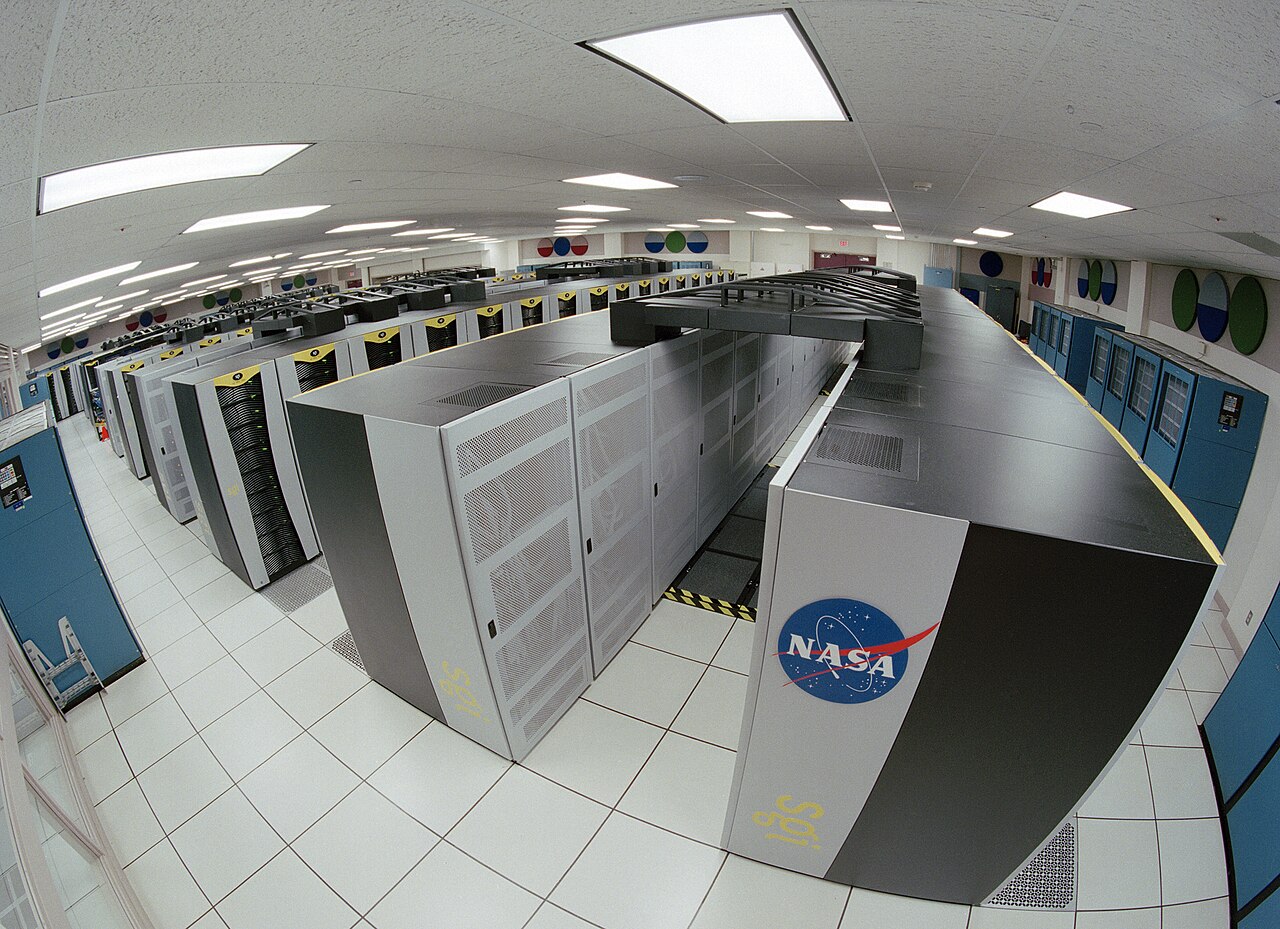
DOJ's November 3 ILC Dover and ILC Astrospace settlement announcement highlights the connection between contractual security requirements, system plans and assessment evidence. The claims remain allegations with no determination of liability.
NIST's November 2 final workshop report identifies supplier evidence, logging and responsibility gaps relevant to federal security policy and incident-response planning.
DHS's October 30 Federal Register publication details an existing Acronis supply-chain security order, with contract-specific implications for federal security policy and system reviews.
A November 2 Marketplace update separates certified and non-certified third-party resources, helping federal security teams examine cloud dependencies.
NIST’s November 4 pre-draft request seeks feedback on cryptographic key-derivation changes by December 18, with implications for federal security assessment planning.
FedRAMP’s November 2 announcement reports the first full CR26-compliant 20x Class C certification, granted October 29. The milestone concerns cloud-security assessment, not an agency ATO or a contract award.
Final NIST IR 8547 connects cryptographic migration planning with federal deadlines and supply-chain dependencies.
From CDG’s Oct 23 company post: For contractors evaluating cloud services, that distinction matters. Check the exact offering’s current designation before relying on a vendor’s general certification claim.…
From CDG’s Oct 23 company post: SP 800-100 Rev. 1 is an initial public draft aligned with CSF 2.0. It covers governance, risk management, incident response and continuous monitoring, helping leaders connect…
From CDG’s Oct 22 company post: NIST’s National Cybersecurity Center of Excellence is accepting feedback on updated DevSecOps project resources through November 9, 2026. Announced September 24, the material…
From CDG’s Oct 22 company post: Published October 22, SP 800-221 Revision 1 connects information and communications technology risk management with enterprise risk decisions and CSF 2.0’s Govern function. It…
From CDG’s Oct 22 company post: PHP's October 21 security release fixes CVE-2026-109618 and CVE-2026-109619 in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. The vulnerabilities can allow remote code execution…
From CDG’s Oct 21 company post: On October 16, NIST, NSA and CISA published ten voluntary practices for incidents during super intelligence (SI) training and evaluation. The primary audience is organizations…
From CDG’s Oct 21 company post: On October 20, CISA added six vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog based on evidence of active exploitation:
From CDG’s Oct 20 company post: Published October 15, RFC-0036 is open for comment through November 19, 2026. These are proposed pilot requirements, not final rules. The proposal concerns the Phase 4…
From CDG’s Oct 21 company post: RFC-0035 opened October 14 and is open for comment through November 17, 2026. It addresses both 20x and Rev5, separately from the Class D cloud-hosted pilot proposal.
Original posts reflect their publication dates. Status, guidance, and deadlines can change. Check the official notice for current amendments and requirements.